We can't read your messages.
This is zero-knowledge architecture: the server is mathematically blind to your content. There is no plaintext of your conversation anywhere but on participating devices in the conversation.
 Chat in Lume Auth · personal app
Chat in Lume Auth uses post-quantum, end-to-end encryption and contacts verified through biometric-derived keys. We cannot read your messages. A live scan protects app access, but cannot guarantee protection after an endpoint is compromised.
 Unlocked by you.
Chat uses post-quantum key establishment and signatures: ML-KEM establishes key material, while ML-DSA signs data. These are distinct functions within the end-to-end encryption design; ML-DSA does not encrypt messages.
Contacts are verified by their biometric-derived keys — so the person on the other end is cryptographically bound to a real, live human, not a recycled phone number or a spoofed handle. The key binds the contact to the enrolled person; it does not by itself establish their legal identity.
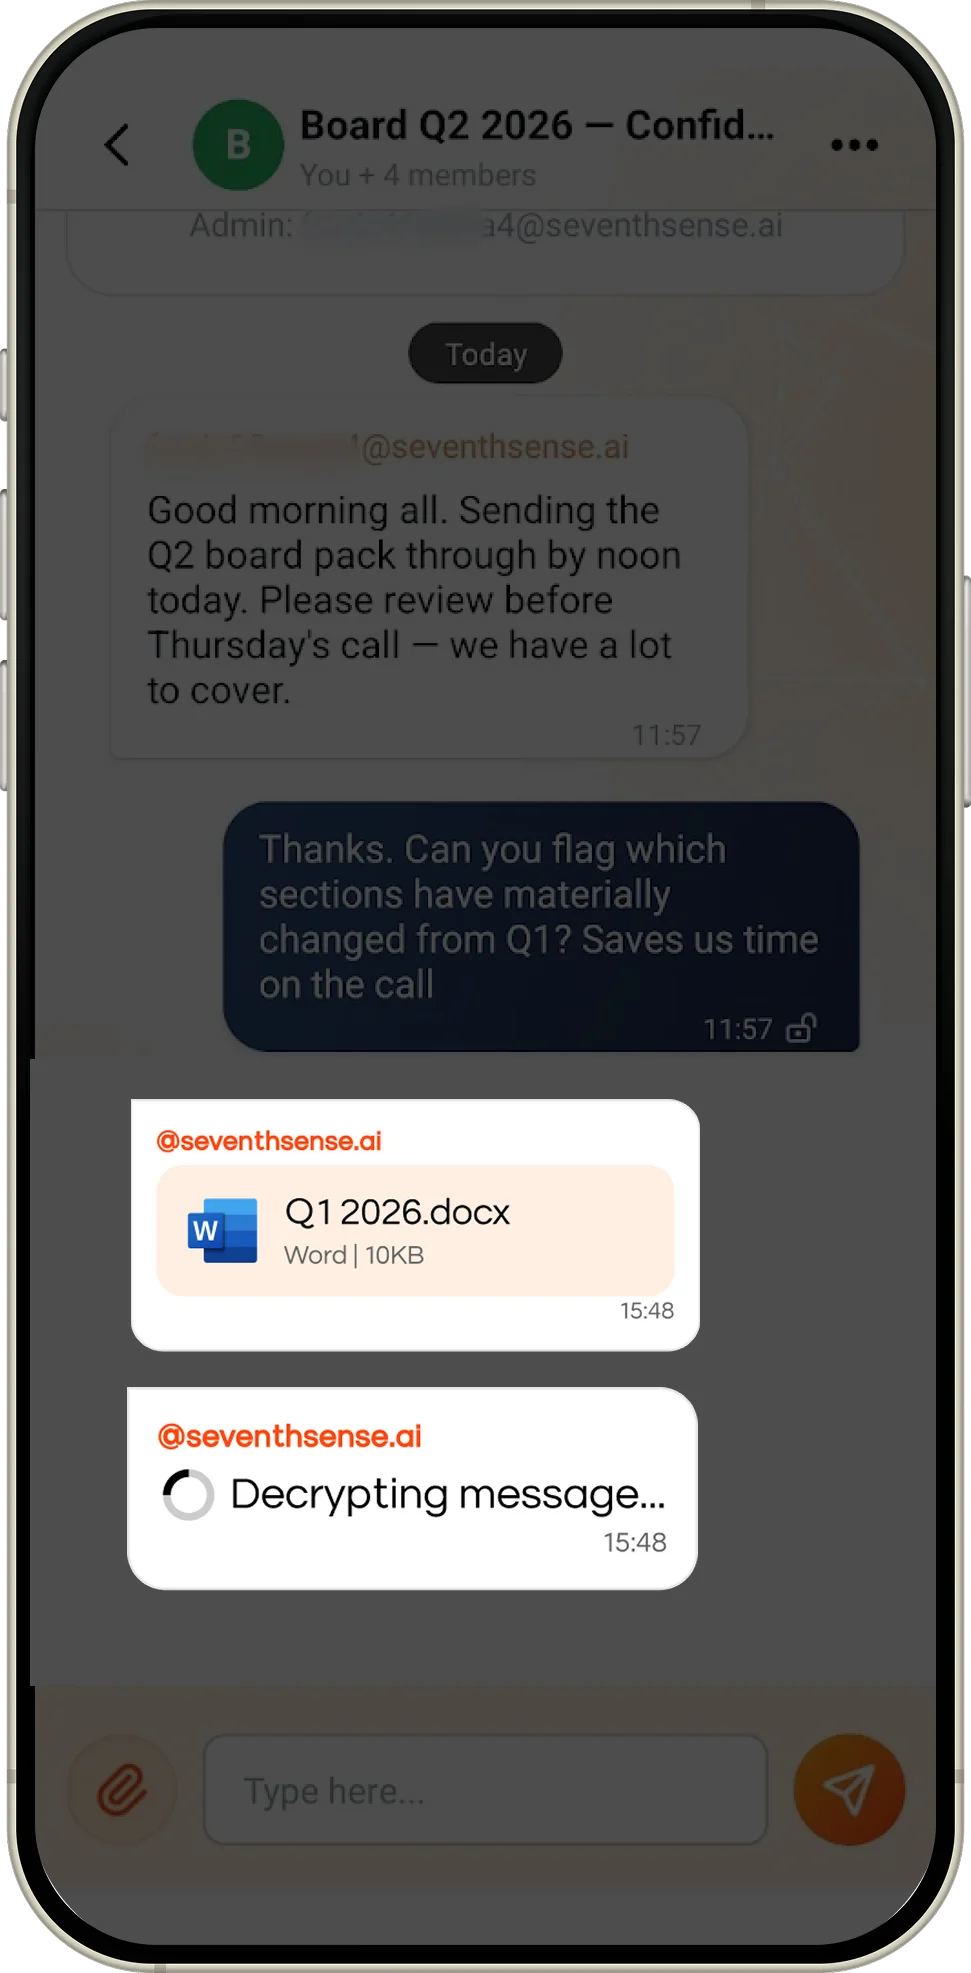
This is zero-knowledge architecture: the server is mathematically blind to your content. There is no plaintext of your conversation anywhere but on participating devices in the conversation.
The app opens only to a live biometric scan. Physical possession alone does not unlock protected messages. No PIN fallback, no master password. A compromised endpoint remains outside that guarantee.
Free on iOS and Android. Your conversations stay yours.
Need MFA, passwords and notes too?Meet Lume Auth